
MineOS's auto-discovery is real-time and continuous, allowing you to monitor any new data source your company interacts with. Data sources will be displayed according to usage and departments within your company.
Before you start
- Make sure you have a MineOS plan that includes system discovery.
- Access to a Microsoft Entra ID account with Global Administrator or Privileged Role Administrator privileges. This role is required to grant consent on behalf of your entire organization — see the note below.
Follow the setup steps:
Step 1 - Login to your MineOS account
Login to your MineOS account and go to: Data Inventory -> Radar -> Radar setup
Step 2 - Azure connection
Under "Single Sign-On" choose "Azure".
Scroll down and click "Sign in with Microsoft" to start the authorization flow
Step 3 - Review and approve the required permissions
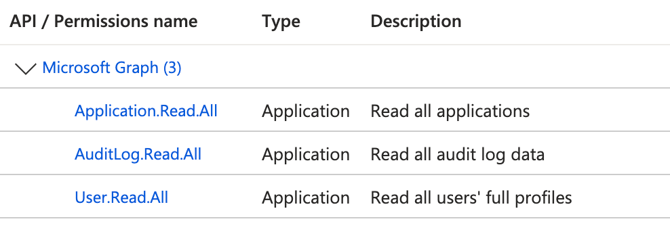
Review and approve the required permissions to complete the flow. This step must be completed by a user with Global Administrator or Privileged Role Administrator privileges — the permissions below require consent for your entire organization, not just the signed-in user.
The required permissions are as follows:
Application.Read.All, AuditLog.Read.All, User.Read.All
Step 4 - Verify admin consent was granted
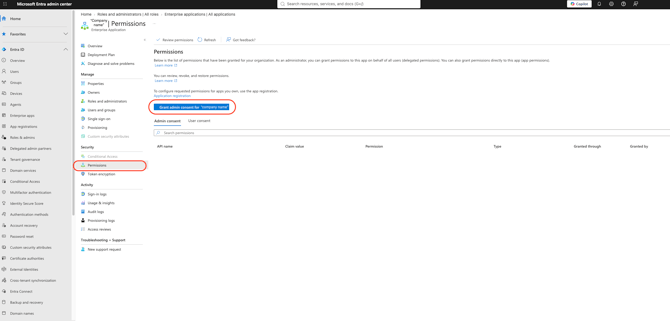
- In the Microsoft Entra admin center, go to Enterprise applications.
- Select the MineOS application.
- Open Permissions.
- Confirm each required permission below shows Admin consent granted, with status Granted for [your organization].
Important: If consent wasn't granted by an admin, or was only granted for a single user, discovery may return little or no data, or the connection may show an error such as "Insufficient privileges to complete the operation."
Step 5 - Reconnecting After a Permissions Fix
If Azure SSO discovery was already connected before admin consent was correctly granted, fixing the consent in Entra alone will not apply retroactively. You'll need to:
- Disconnect the existing Azure connection under Data Inventory → Radar → Radar setup.
- Reconnect by selecting Azure again and signing in with an account that has completed admin consent, as described above.
Discovery will restart using the corrected permissions.
Note: If you are not an admin on Azure, you will see a screen that allows you to submit a request for approval. You can submit the request and it will automatically be sent to your IT department.
Once they approve your request, you will be able to click this button again to complete the connection process.
That's it! you are done. Discovery will automatically start.